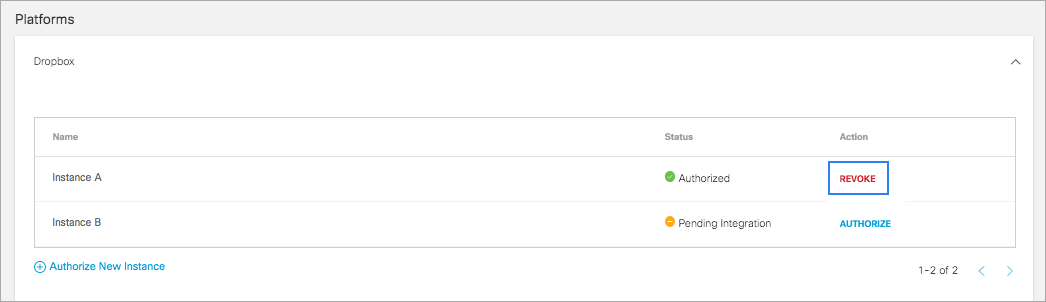
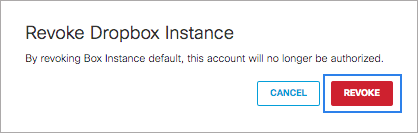
Describes Manage Cloud Malware Protection in Cisco Secure Access. Cloud Malware Protection scans your environment's cloud platforms for malicious files and any other risks.
Cloud Malware Protection scans your environment's cloud platforms for malicious files and any other risks. You can enable more than one instance of a platform. For example, a school administration with an instance of Box for teachers and faculty and another for students can enable both instances, the result being complete malware protection for Box.
When you authenticate a tenant for Cloud Malware protection, the scan begins immediately and inspects new and updated files as changes occur. Additionally, one week after the tenant is authenticated Cloud Malware also initiates a retroactive scan of all existing files for the tenant going back in time as far as recorded. The time it takes to complete the retroactive scan depends on the number of files in the tenants and their size and on the API rate limit of the platform vendor.
For Microsoft Outlook, Cloud Malware protection applies to the primary inbox only. For outgoing mail you can enable Data Loss Prevention; see Enable SaaS API Data Loss Prevention for Microsoft 365 Tenants.
When Cloud Malware Protection finds malicious files, the information is presented in the Cloud Malware Report. You can remediate potential risk by configuring a response action that Secure Access will automatically apply for malicious files detected within the tenant:
-
For all platforms you can choose to monitor the file.
-
For Webex Teams and Slack you can choose to delete the file.
-
For Dropbox, Box, Microsoft 365, SharePoint, Microsoft 365 OneDrive, and Google you can quarantine the file.
-
The quarantined file is moved into a folder named Cisco_Quarantine_Malware in the root path of the admin who authorized the tenant, removes all collaborators, and changes the file owner to the platform admin.
-
A text file is left in the original location of the quarantined file with the name
filename.ppt_Cisco_Quarantined.txtexplaining to the original file owner that the file is identified as malware or exposing sensitive data, and for more information to contact their organization administrator.
-
-
For ServiceNow you can choose to quarantine the file.
-
The file is moved into a table named Cisco_Quarantine_Malware which can be access only by the admin user who authorized the ServiceNow tenant.
-
A footprint is attached to the notes\activities area of the table the file is attached to. This footprint will notify users that the file has been identified as malware, and for more information they should contact their administrator.
-
-
For Salesforce (uploaded files as well as files attached to chatter posts) you can choose to quarantine the file.
-
The system will remove all collaborators and change the file owner to the Salesforce admin who has performed the authorization, and who has been assigned the permission set for the quarantine app. In Salesforce, the admin can see a list of quarantined files by using the App Launcher to search for "Cisco Secure Access SF Quarantine," then selecting the All Quarantines option.

Click on the listing for an individual file to see the information about it:

-
The system replaces the file in its original location with a text file named
filename_Cisco_Quarantined.txtexplaining to the original file owner that the file is identified as malware and for more information to contact their organization administrator.
-
-
Quarantine attempts may fail if the files have been locked or blocked by settings within their native platforms. Settings local to the platform where a file resides take precedence over Secure Access' ability to detect or remediate DLP violations or malware.
You can configure each Cloud Malware instance to automatically apply a response action to malicious files when they are detected, or you can manually trigger a response action from the Cloud Malware report. For more information, see Cloud Malware Report.